Golden service: one year service warrant after sale
If you purchase our CKS: Certified Kubernetes Security Specialist (CKS) test questions materials, we guarantee our products are valid for one year. You can download our latest materials free of charge within one year if we release new CKS test questions. If you are ready to purchase test engine, please rest assured that we will serve for ever user within one year before passing test.
Linux Foundation CKS Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
Reference: https://training.linuxfoundation.org/certification/certified-kubernetes-security-specialist/#exams
How can you get valid CKS: Certified Kubernetes Security Specialist (CKS) test questions for passing exam? Many candidates are looking for valid test online to pass exam day to day. Here is your chance. Testpassed offers the best high passing rate CKS test online to help candidates pass exam for sure. We are engaged in editing good test questions materials so many years. Our educational experts all have more than 8 years' experience in IT career certifications. Our CKS: Certified Kubernetes Security Specialist (CKS) test questions are edited seriously and strictly. We guarantee our products help most of candidates pass test. If users pay much attention to our Linux Foundation CKS test questions most of users will get good passing score.
Golden service: 7/24 online service support
We support 7/24 online customer service even on large official holiday. No matter when candidates have any problem & advice about CKS: Certified Kubernetes Security Specialist (CKS) test questions materials we are sure to reply and solve with you soon. Service staff performance assess criteria are required that any email and contact about CKS test engine should be handled in two hours.
Three versions of excellent products: PDF version, Soft version, APP version
We release three versions of CKS: Certified Kubernetes Security Specialist (CKS) test questions materials. Different kinds of products satisfy different demands of people. If you like writing and reading on paper, PDF version of CKS test questions are suitable for you. If you like studying on computer you can choose soft version or/and APP version.
These two versions of CKS test engine have some similar functions: timed test, mark your performance, point out wrong questions and remind you of practicing many times. Soft version of CKS: Certified Kubernetes Security Specialist (CKS) test questions are downloaded and installed in personal computers (Windows operating system and Java environment). APP version of CKS test questions are based on WEB browser, it supports Windows / Mac / Android / iOS etc.
Soft version of CKS: Certified Kubernetes Security Specialist (CKS) test questions can be downloaded in more than 200 personal computers. Once you download software, you use it offline any time. If there is no network, you can copy on another computer. APP version of CKS test questions are downloaded and installed well. It is based on web browser, if you do not close website, you can also use it offline. As to functional performance APP version of Linux Foundation CKS test exam materials may be much stabler than Soft version.
We guarantee that No Pass No Pay
We are confident about our CKS: Certified Kubernetes Security Specialist (CKS) test questions materials that we can help users pass real test certainly. Our passing rate for Linux Foundation Kubernetes Security Specialist exam is 99.69%. Most candidates will clear exam successfully. We make sure that if you fail exam sadly we will full refund to you unconditionally. If candidates send us your unqualified score scanned, we will refund to you directly. Please trust our CKS: Certified Kubernetes Security Specialist (CKS) test questions. If you choose us, we will help you success surely.
After purchase, Instant Download: Upon successful payment, Our systems will automatically send the product you have purchased to your mailbox by email. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
Linux Foundation Certified Kubernetes Security Specialist (CKS) Sample Questions:
SIMULATION
Create a PSP that will only allow the persistentvolumeclaim as the volume type in the namespace restricted.
Create a new PodSecurityPolicy named prevent-volume-policy which prevents the pods which is having different volumes mount apart from persistentvolumeclaim.
Create a new ServiceAccount named psp-sa in the namespace restricted.
Create a new ClusterRole named psp-role, which uses the newly created Pod Security Policy prevent-volume-policy Create a new ClusterRoleBinding named psp-role-binding, which binds the created ClusterRole psp-role to the created SA psp-sa.
Hint:
Also, Check the Configuration is working or not by trying to Mount a Secret in the pod maifest, it should get failed.
POD Manifest:
apiVersion: v1
kind: Pod
metadata:
name:
spec:
containers:
- name:
image:
volumeMounts:
- name:
mountPath:
volumes:
- name:
secret:
secretName:
Correct Answer:
See the Explanation belowExplanation:
apiVersion: policy/v1beta1
kind: PodSecurityPolicy
metadata:
name: restricted
annotations:
seccomp.security.alpha.kubernetes.io/allowedProfileNames: 'docker/default,runtime/default' apparmor.security.beta.kubernetes.io/allowedProfileNames: 'runtime/default' seccomp.security.alpha.kubernetes.io/defaultProfileName: 'runtime/default' apparmor.security.beta.kubernetes.io/defaultProfileName: 'runtime/default' spec:
privileged: false
# Required to prevent escalations to root.
allowPrivilegeEscalation: false
# This is redundant with non-root + disallow privilege escalation,
# but we can provide it for defense in depth.
requiredDropCapabilities:
- ALL
# Allow core volume types.
volumes:
- 'configMap'
- 'emptyDir'
- 'projected'
- 'secret'
- 'downwardAPI'
# Assume that persistentVolumes set up by the cluster admin are safe to use.
- 'persistentVolumeClaim'
hostNetwork: false
hostIPC: false
hostPID: false
runAsUser:
# Require the container to run without root privileges.
rule: 'MustRunAsNonRoot'
seLinux:
# This policy assumes the nodes are using AppArmor rather than SELinux.
rule: 'RunAsAny'
supplementalGroups:
rule: 'MustRunAs'
ranges:
# Forbid adding the root group.
- min: 1
max: 65535
fsGroup:
rule: 'MustRunAs'
ranges:
# Forbid adding the root group.
- min: 1
max: 65535
readOnlyRootFilesystem: false
SIMULATION
Documentation
Installing the Sidecar, PeerAuthentication, Deployments
You must connect to the correct host . Failure to do so may result in a zero score.
[candidate@base] $ ssh cks000041
Context
A microservices-based application using unencrypted Layer 4 (L4) transport must be secured with Istio.
Task
Perform the following tasks to secure an existing application's Layer 4 (L4) transport communication using Istio.
Istio is installed to secure Layer 4 (L4) communications.
You may use your browser to access Istio's documentation.
First, ensure that all Pods in the mtls namespace have the istio-proxy sidecar injected.
Next, configure mutual authentication in strict mode for all workloads in the mtls namespace.
Correct Answer:
See the Explanation below for complete solution
Explanation:
Below is the CKS exam-ready, step-by-step solution for QUESTION 15.
Follow exactly in this order. No extra changes.
QUESTION 15 - Istio mTLS (EXAM MODE)
1) Connect to the correct host
ssh cks000041
sudo -i
export KUBECONFIG=/etc/kubernetes/admin.conf
2) Ensure sidecar injection is enabled for the mtls namespace
2.1 Check current namespace labels
kubectl get ns mtls --show-labels
2.2 Enable automatic Istio sidecar injection
kubectl label namespace mtls istio-injection=enabled --overwrite
Verify:
kubectl get ns mtls --show-labels | grep istio-injection
Expected:
istio-injection=enabled
3) Ensure ALL Pods get the istio-proxy sidecar
Existing Pods will not get sidecars automatically.
You must restart workloads in the namespace.
3.1 Restart all Deployments in mtls
kubectl -n mtls rollout restart deployment
3.2 Verify Pods now have 2 containers (app + istio-proxy)
kubectl -n mtls get pods
Then check one Pod:
kubectl -n mtls get pod <pod-name> -o jsonpath='{.spec.containers[*].name}{"\n"}' Expected output includes:
istio-proxy
4) Configure mutual TLS (mTLS) in STRICT mode
4.1 Create a PeerAuthentication for the mtls namespace
cat <<EOF | kubectl apply -f -
apiVersion: security.istio.io/v1beta1
kind: PeerAuthentication
metadata:
name: mtls-strict
namespace: mtls
spec:
mtls:
mode: STRICT
EOF
5) Verify mTLS policy is applied
kubectl -n mtls get peerauthentication
kubectl -n mtls describe peerauthentication mtls-strict
Expected:
Mode: STRICT
6) Final verification (exam confidence check)
6.1 Confirm all Pods are Running
kubectl -n mtls get pods
6.2 Confirm sidecar injection everywhere
kubectl -n mtls get pods -o jsonpath='{range .items[*]}{.metadata.name}{" -> "}{.spec.containers[*].name}{"\n"}{end}' Each line must include istio-proxy.
SIMULATION
You must complete this task on the following cluster/nodes:
Cluster: trace
Master node: master
Worker node: worker1
You can switch the cluster/configuration context using the following command:
[desk@cli] $ kubectl config use-context trace
Given: You may use Sysdig or Falco documentation.
Task:
Use detection tools to detect anomalies like processes spawning and executing something weird frequently in the single container belonging to Pod tomcat.
Two tools are available to use:
1. falco
2. sysdig
Tools are pre-installed on the worker1 node only.
Analyse the container's behaviour for at least 40 seconds, using filters that detect newly spawning and executing processes.
Store an incident file at /home/cert_masters/report, in the following format:
[timestamp],[uid],[processName]
Note: Make sure to store incident file on the cluster's worker node, don't move it to master node.
Correct Answer:
See the Explanation below
Explanation:
$vim /etc/falco/falco_rules.local.yaml
- rule: Container Drift Detected (open+create)
desc: New executable created in a container due to open+create
condition: >
evt.type in (open,openat,creat) and
evt.is_open_exec=true and
container and
not runc_writing_exec_fifo and
not runc_writing_var_lib_docker and
not user_known_container_drift_activities and
evt.rawres>=0
output: >
%evt.time,%user.uid,%proc.name # Add this/Refer falco documentation
priority: ERROR
$kill -1 <PID of falco>
Explanation:
[desk@cli] $ ssh node01
[node01@cli] $ vim /etc/falco/falco_rules.yaml
search for Container Drift Detected & paste in falco_rules.local.yaml
[node01@cli] $ vim /etc/falco/falco_rules.local.yaml
- rule: Container Drift Detected (open+create)
desc: New executable created in a container due to open+create
condition: >
evt.type in (open,openat,creat) and
evt.is_open_exec=true and
container and
not runc_writing_exec_fifo and
not runc_writing_var_lib_docker and
not user_known_container_drift_activities and
evt.rawres>=0
output: >
%evt.time,%user.uid,%proc.name # Add this/Refer falco documentation
priority: ERROR
[node01@cli] $ vim /etc/falco/falco.yaml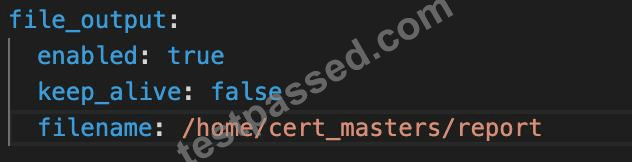
SIMULATION
Create a network policy named allow-np, that allows pod in the namespace staging to connect to port 80 of other pods in the same namespace.
Ensure that Network Policy:-
1. Does not allow access to pod not listening on port 80.
2. Does not allow access from Pods, not in namespace staging.
Correct Answer:
See the Explanation belowExplanation:
apiVersion: networking.k8s.io/v1
kind: NetworkPolicy
metadata:
name: network-policy
spec:
podSelector: {} #selects all the pods in the namespace deployed
policyTypes:
- Ingress
ingress:
- ports: #in input traffic allowed only through 80 port only
- protocol: TCP
port: 80
SIMULATION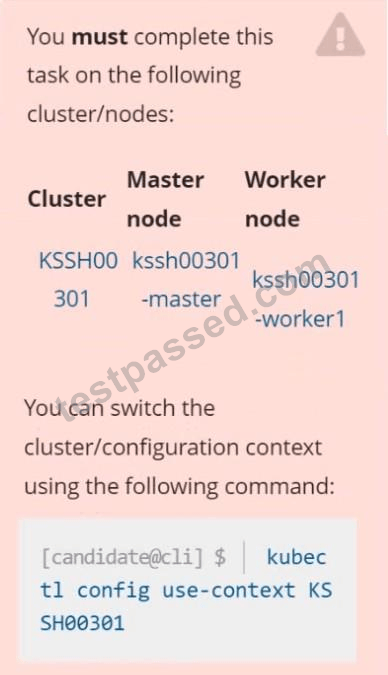
Task
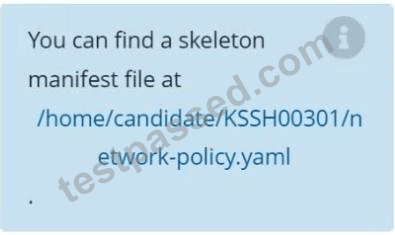
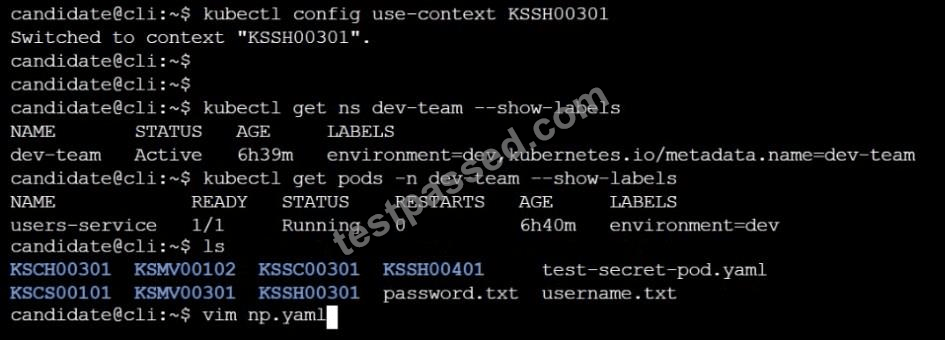
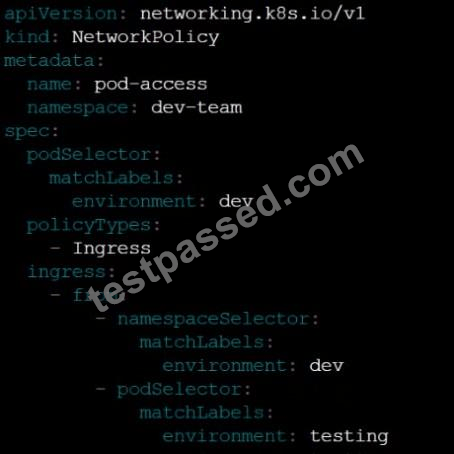
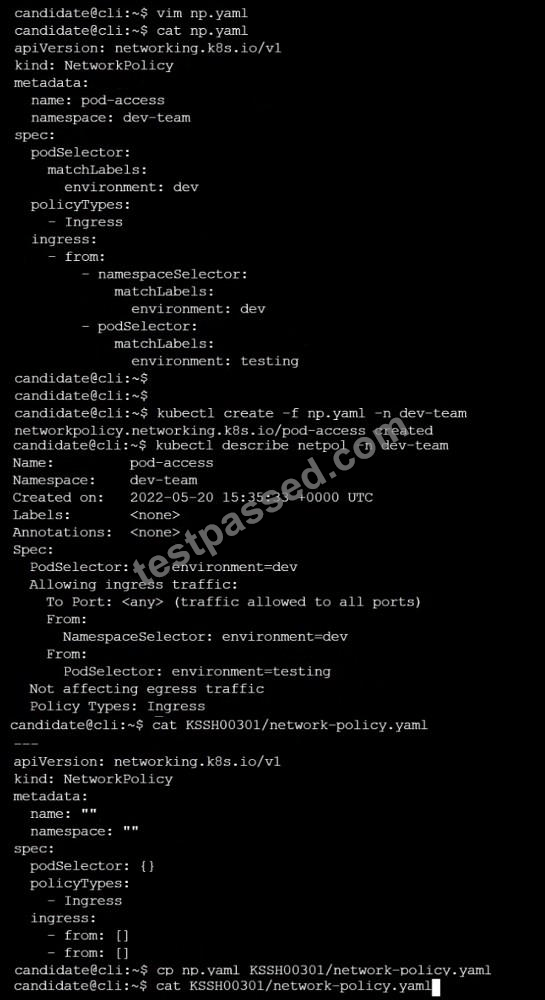
Create a NetworkPolicy named pod-access to restrict access to Pod users-service running in namespace dev-team.
Only allow the following Pods to connect to Pod users-service:
Correct Answer:

Viewing page 1 out of 14 pages.
Viewing questions 1-5 out of 66 questions.


 Mavis

 Martha

 Truman
 Suzanne

 Agnes
 Edgar
 Ingrid
 Justin
 Meredith
 Harry
 Jeremy
 Matthew
 Chasel
 Martha
 Penelope