How can you get valid Professional-Cloud-Security-Engineer: Google Cloud Certified - Professional Cloud Security Engineer Exam test questions for passing exam? Many candidates are looking for valid test online to pass exam day to day. Here is your chance. Testpassed offers the best high passing rate Professional-Cloud-Security-Engineer test online to help candidates pass exam for sure. We are engaged in editing good test questions materials so many years. Our educational experts all have more than 8 years' experience in IT career certifications. Our Professional-Cloud-Security-Engineer: Google Cloud Certified - Professional Cloud Security Engineer Exam test questions are edited seriously and strictly. We guarantee our products help most of candidates pass test. If users pay much attention to our Google Professional-Cloud-Security-Engineer test questions most of users will get good passing score.
Golden service: one year service warrant after sale
If you purchase our Professional-Cloud-Security-Engineer: Google Cloud Certified - Professional Cloud Security Engineer Exam test questions materials, we guarantee our products are valid for one year. You can download our latest materials free of charge within one year if we release new Professional-Cloud-Security-Engineer test questions. If you are ready to purchase test engine, please rest assured that we will serve for ever user within one year before passing test.
Configure Network Security
- Private Connectivity Establishment: The consideration for this topic includes enabling private connectivity between Google APIs and VPC as well as private RFC 1918 connectivity between Google Cloud Projects & VPC networks and between VPC network & data centers.
- Network Segmentation Configuration: This part evaluates one’s competence in network perimeter controls, and load balancing, including global, SSL proxy, network, TCP load balancer, and HTTP(S);
- Network Security Design: The test takers will be required to demonstrate an understanding of security properties of VPC networks, shared VPC, firewall rules, and VPC peering. This objective also measures their skills in using DNSSEC, security policy for app-to-app, and network isolation & data encapsulation for N-tier application design;
For more information visit:
Google Professional Cloud Security Engineer Exam Reference
Reference: https://cloud.google.com/certification/cloud-security-engineer
What is Google Professional Cloud Security Engineer Exam
The Google Professional Cloud Security Engineer is a private administrator responsible for helping organizations define and enforce a highly secure infrastructure on the Google Cloud Platform (GCP). GCP's professional cloud security Engineer uses an in-depth understanding of security and safety best practices, as well as an in-depth understanding of market security needs.
The cloud security designer brings his knowledge to the design, advancement, and management of the framework through Google security innovations. The GCP Cloud Security Engineer Certification Exam helps validate an individual's proficiency in various skills. Skills and areas of understanding include identifying and tracking access, as well as using Google security technologies to ensure data protection.
The certification exam will no doubt also assess candidates' abilities to configure network security measures and collect and evaluate Google Cloud logs. In addition, the role of a cloud security designer also includes event response management and a broader understanding of regulatory policies.
We guarantee that No Pass No Pay
We are confident about our Professional-Cloud-Security-Engineer: Google Cloud Certified - Professional Cloud Security Engineer Exam test questions materials that we can help users pass real test certainly. Our passing rate for Google Google Cloud Certified exam is 99.69%. Most candidates will clear exam successfully. We make sure that if you fail exam sadly we will full refund to you unconditionally. If candidates send us your unqualified score scanned, we will refund to you directly. Please trust our Professional-Cloud-Security-Engineer: Google Cloud Certified - Professional Cloud Security Engineer Exam test questions. If you choose us, we will help you success surely.
After purchase, Instant Download: Upon successful payment, Our systems will automatically send the product you have purchased to your mailbox by email. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
Golden service: 7/24 online service support
We support 7/24 online customer service even on large official holiday. No matter when candidates have any problem & advice about Professional-Cloud-Security-Engineer: Google Cloud Certified - Professional Cloud Security Engineer Exam test questions materials we are sure to reply and solve with you soon. Service staff performance assess criteria are required that any email and contact about Professional-Cloud-Security-Engineer test engine should be handled in two hours.
Three versions of excellent products: PDF version, Soft version, APP version
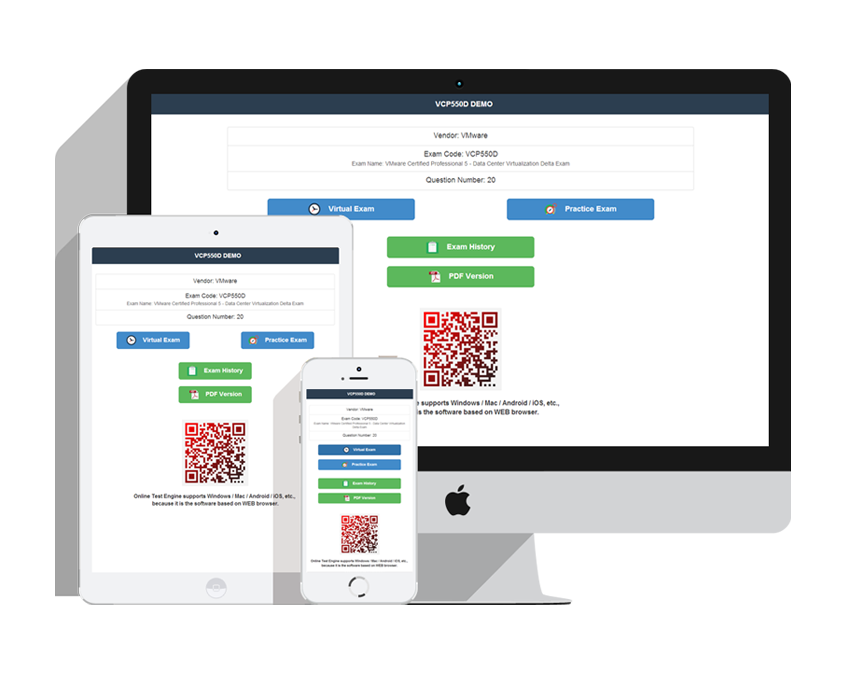
We release three versions of Professional-Cloud-Security-Engineer: Google Cloud Certified - Professional Cloud Security Engineer Exam test questions materials. Different kinds of products satisfy different demands of people. If you like writing and reading on paper, PDF version of Professional-Cloud-Security-Engineer test questions are suitable for you. If you like studying on computer you can choose soft version or/and APP version.
These two versions of Professional-Cloud-Security-Engineer test engine have some similar functions: timed test, mark your performance, point out wrong questions and remind you of practicing many times. Soft version of Professional-Cloud-Security-Engineer: Google Cloud Certified - Professional Cloud Security Engineer Exam test questions are downloaded and installed in personal computers (Windows operating system and Java environment). APP version of Professional-Cloud-Security-Engineer test questions are based on WEB browser, it supports Windows / Mac / Android / iOS etc.
Soft version of Professional-Cloud-Security-Engineer: Google Cloud Certified - Professional Cloud Security Engineer Exam test questions can be downloaded in more than 200 personal computers. Once you download software, you use it offline any time. If there is no network, you can copy on another computer. APP version of Professional-Cloud-Security-Engineer test questions are downloaded and installed well. It is based on web browser, if you do not close website, you can also use it offline. As to functional performance APP version of Google Professional-Cloud-Security-Engineer test exam materials may be much stabler than Soft version.
Google Professional-Cloud-Security-Engineer Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Ensuring data protection | 23% | - Protecting sensitive data and preventing data loss
|
| Configuring access | 25% | - Managing Cloud Identity
|
| Supporting compliance requirements | 14% | - Determining security requirements
|
| Configuring network security | 19% | - Designing network security
|
| Managing operations | 19% | - Automating infrastructure and application security
|
Google Cloud Certified - Professional Cloud Security Engineer Sample Questions:
How should a customer reliably deliver Stackdriver logs from GCP to their on-premises SIEM system?
- A. Configure Organizational Log Sinks to export logs to a Cloud Pub/Sub Topic, which will be sent to the SIEM via Dataflow.
- B. Configure every project to export all their logs to a common BigQuery DataSet, which will be queried by the SIEM system.
- C. Build a connector for the SIEM to query for all logs in real time from the GCP RESTful JSON APIs.
- D. Send all logs to the SIEM system via an existing protocol such as syslog.
Correct Answer: A 🗳️
Explanation: Only visible for TestPassed members. You can sign-up / login (it's free).
A customer deploys an application to App Engine and needs to check for Open Web Application Security Project (OWASP) vulnerabilities.
Which service should be used to accomplish this?
- A. Cloud Armor
- B. Google Cloud Audit Logs
- C. Forseti Security
- D. Cloud Security Scanner
Correct Answer: D 🗳️
Explanation: Only visible for TestPassed members. You can sign-up / login (it's free).
You have a highly sensitive BigQuery workload that contains personally identifiable information (Pll) that you want to ensure is not accessible from the internet. To prevent data exfiltration only requests from authorized IP addresses are allowed to query your BigQuery tables.
What should you do?
- A. Use the Restrict Resource service usage organization policy constraint along with Cloud Data Loss Prevention (DLP).
- B. Use service perimeter and create an access level based on the authorized source IP address as the condition.
- C. Use Google Cloud Armor security policies defining an allowlist of authorized IP addresses at the global HTTPS load balancer.
- D. Use the Restrict allowed Google Cloud APIs and services organization policy constraint along with Cloud Data Loss Prevention (DLP).
Correct Answer: B 🗳️
Explanation: Only visible for TestPassed members. You can sign-up / login (it's free).
Your company has multiple teams needing access to specific datasets across various Google Cloud data services for different projects. You need to ensure that team members can only access the data relevant to their projects and prevent unauthorized access to sensitive information within BigQuery, Cloud Storage, and Cloud SQL. What should you do?
- A. Use VPC Service Controls to create security perimeters around the projects for BigQuery. Cloud Storage, and Cloud SQL services. restricting access based on the network origin of the requests.
- B. Enable project-level data access logs for BigQuery. Cloud Storage, and Cloud SQL. Configure log sinks to export these logs to Security Command Center to identify unauthorized access attempts.
- C. Grant project-level group permissions by using specific Cloud IAM roles. Use BigQuery authorized views. Cloud Storage uniform bucket-level access, and Cloud SQL database roles.
- D. Configure an access level to control access to the Google Cloud console for users managing these data services. Require multi-factor authentication for all access attempts.
Correct Answer: C 🗳️
Explanation: Only visible for TestPassed members. You can sign-up / login (it's free).
Your company is migrating a customer database that contains personally identifiable information (PII) to Google Cloud. To prevent accidental exposure, this data must be protected at rest. You need to ensure that all PII is automatically discovered and redacted, or pseudonymized, before any type of analysis. What should you do?
- A. Implement Cloud Armor to protect the database from external threats and configure firewall rules to restrict network access to only authorized internal IP addresses.
- B. Use Cloud KMS to encrypt the database at rest with a customer-managed encryption key (CMEK).
Implement VPC Service Controls. - C. Create Cloud Storage buckets with object versioning enabled, and use IAM policies to restrict access to the data. Use Data Loss Prevention API (DLP API) on the buckets to scan for sensitive data and generate detection alerts.9
- D. Configure Sensitive Data Protection to scan the database for PII using both predefined and custom infoTypes and to mask sensitive data.8
Correct Answer: D 🗳️
Explanation: Only visible for TestPassed members. You can sign-up / login (it's free).
Viewing page 1 out of 64 pages.
Viewing questions 1-5 out of 320 questions.


 Sampson

 Larry

 Doreen

 Murray
 Constance
 Carr
 Miranda
 Jack
 Zenobia
 Ivy
 Clifford
 Derrick
 William
 Howar
 Isidore
 Dave
 Edgar
 Patrick