How can you get valid ISOIEC20000LI: Beingcert ISO/IEC 20000 Lead Implementer Exam test questions for passing exam? Many candidates are looking for valid test online to pass exam day to day. Here is your chance. Testpassed offers the best high passing rate ISOIEC20000LI test online to help candidates pass exam for sure. We are engaged in editing good test questions materials so many years. Our educational experts all have more than 8 years' experience in IT career certifications. Our ISOIEC20000LI: Beingcert ISO/IEC 20000 Lead Implementer Exam test questions are edited seriously and strictly. We guarantee our products help most of candidates pass test. If users pay much attention to our ISO ISOIEC20000LI test questions most of users will get good passing score.
Three versions of excellent products: PDF version, Soft version, APP version
We release three versions of ISOIEC20000LI: Beingcert ISO/IEC 20000 Lead Implementer Exam test questions materials. Different kinds of products satisfy different demands of people. If you like writing and reading on paper, PDF version of ISOIEC20000LI test questions are suitable for you. If you like studying on computer you can choose soft version or/and APP version.
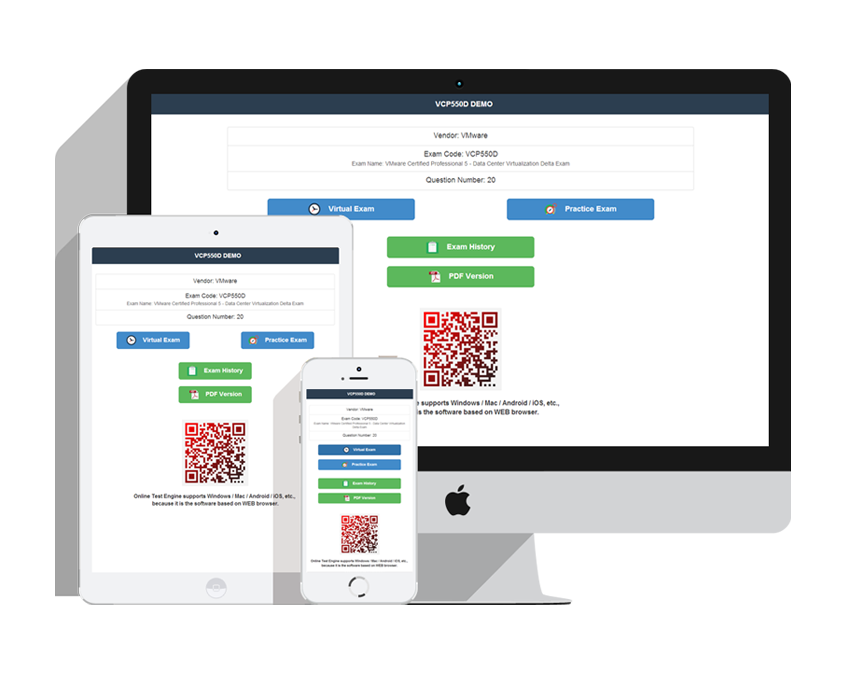
These two versions of ISOIEC20000LI test engine have some similar functions: timed test, mark your performance, point out wrong questions and remind you of practicing many times. Soft version of ISOIEC20000LI: Beingcert ISO/IEC 20000 Lead Implementer Exam test questions are downloaded and installed in personal computers (Windows operating system and Java environment). APP version of ISOIEC20000LI test questions are based on WEB browser, it supports Windows / Mac / Android / iOS etc.
Soft version of ISOIEC20000LI: Beingcert ISO/IEC 20000 Lead Implementer Exam test questions can be downloaded in more than 200 personal computers. Once you download software, you use it offline any time. If there is no network, you can copy on another computer. APP version of ISOIEC20000LI test questions are downloaded and installed well. It is based on web browser, if you do not close website, you can also use it offline. As to functional performance APP version of ISO ISOIEC20000LI test exam materials may be much stabler than Soft version.
We guarantee that No Pass No Pay
We are confident about our ISOIEC20000LI: Beingcert ISO/IEC 20000 Lead Implementer Exam test questions materials that we can help users pass real test certainly. Our passing rate for ISO ISO/IEC 20000 Lead Implementer exam is 99.69%. Most candidates will clear exam successfully. We make sure that if you fail exam sadly we will full refund to you unconditionally. If candidates send us your unqualified score scanned, we will refund to you directly. Please trust our ISOIEC20000LI: Beingcert ISO/IEC 20000 Lead Implementer Exam test questions. If you choose us, we will help you success surely.
After purchase, Instant Download: Upon successful payment, Our systems will automatically send the product you have purchased to your mailbox by email. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
Golden service: 7/24 online service support
We support 7/24 online customer service even on large official holiday. No matter when candidates have any problem & advice about ISOIEC20000LI: Beingcert ISO/IEC 20000 Lead Implementer Exam test questions materials we are sure to reply and solve with you soon. Service staff performance assess criteria are required that any email and contact about ISOIEC20000LI test engine should be handled in two hours.
Golden service: one year service warrant after sale
If you purchase our ISOIEC20000LI: Beingcert ISO/IEC 20000 Lead Implementer Exam test questions materials, we guarantee our products are valid for one year. You can download our latest materials free of charge within one year if we release new ISOIEC20000LI test questions. If you are ready to purchase test engine, please rest assured that we will serve for ever user within one year before passing test.
ISO ISOIEC20000LI Exam Syllabus Topics:
| Section | Objectives |
|---|---|
| Topic 1: Fundamental Principles and Concepts of Service Management Systems | - Service Management System Concepts
|
| Topic 2: Preparation for Certification Audit | - Certification Readiness
|
| Topic 3: Continual Improvement | - Improvement Activities
|
| Topic 4: Implementing an SMS Based on ISO/IEC 20000 | - Service Management Processes
|
| Topic 5: Monitoring and Measurement of an SMS | - Performance Evaluation
|
| Topic 6: Planning an SMS Implementation | - Implementation Planning
|
| Topic 7: Service Management System Requirements | - ISO/IEC 20000 Requirements
|
ISO Beingcert ISO/IEC 20000 Lead Implementer Sample Questions:
Based on scenario 8. how does the HealthGenic's negligence affect the ISMS certificate?
- A. HealthGenic might not be able to renew the ISMS certificate, as it has not conducted management reviews at planned intervals
- B. HealthGenic will be able to renew the ISMS certificate, as they did not detect any information security incident in the past two years
- C. HealthGenic might not be able to renew the ISMS certificate, as the internal audit lasted longer than planned
Correct Answer: A 🗳️
Scenario 4: TradeB. a commercial bank that has just entered the market, accepts deposits from its clients and offers basic financial services and loans for investments. TradeB has decided to implement an information security management system (ISMS) based on ISO/IEC 27001 Having no experience of a management
[^system implementation, TradeB's top management contracted two experts to direct and manage the ISMS implementation project.
First, the project team analyzed the 93 controls of ISO/IEC 27001 Annex A and listed only the security controls deemed applicable to the company and their objectives Based on this analysis, they drafted the Statement of Applicability. Afterward, they conducted a risk assessment, during which they identified assets, such as hardware, software, and networks, as well as threats and vulnerabilities, assessed potential consequences and likelihood, and determined the level of risks based on three nonnumerical categories (low, medium, and high). They evaluated the risks based on the risk evaluation criteria and decided to treat only the high risk category They also decided to focus primarily on the unauthorized use of administrator rights and system interruptions due to several hardware failures by establishing a new version of the access control policy, implementing controls to manage and control user access, and implementing a control for ICT readiness for business continuity Lastly, they drafted a risk assessment report, in which they wrote that if after the implementation of these security controls the level of risk is below the acceptable level, the risks will be accepted Which of the actions presented in scenario 4 is NOT compliant with the requirements of ISO/IEC 27001?
- A. TradeB selected only ISO/IEC 27001 controls deemed applicable to the company
- B. The Statement of Applicability was drafted before conducting the risk assessment
- C. The external experts selected security controls and drafted the Statement of Applicability
Correct Answer: B 🗳️
Explanation: Only visible for TestPassed members. You can sign-up / login (it's free).
Scenario 4: TradeB. a commercial bank that has just entered the market, accepts deposits from its clients and offers basic financial services and loans for investments. TradeB has decided to implement an information security management system (ISMS) based on ISO/IEC 27001 Having no experience of a management
[^system implementation, TradeB's top management contracted two experts to direct and manage the ISMS implementation project.
First, the project team analyzed the 93 controls of ISO/IEC 27001 Annex A and listed only the security controls deemed applicable to the company and their objectives Based on this analysis, they drafted the Statement of Applicability. Afterward, they conducted a risk assessment, during which they identified assets, such as hardware, software, and networks, as well as threats and vulnerabilities, assessed potential consequences and likelihood, and determined the level of risks based on three nonnumerical categories (low, medium, and high). They evaluated the risks based on the risk evaluation criteria and decided to treat only the high risk category They also decided to focus primarily on the unauthorized use of administrator rights and system interruptions due to several hardware failures by establishing a new version of the access control policy, implementing controls to manage and control user access, and implementing a control for ICT readiness for business continuity Lastly, they drafted a risk assessment report, in which they wrote that if after the implementation of these security controls the level of risk is below the acceptable level, the risks will be accepted Based on scenario 4, what type of assets were identified during risk assessment?
- A. Business assets
- B. Supporting assets
- C. Primary assets
Correct Answer: B 🗳️
Explanation: Only visible for TestPassed members. You can sign-up / login (it's free).
FinanceX, a well-known financial institution, uses an online banking platform that enables clients to easily and securely access their bank accounts. To log in, clients are required to enter the one-lime authorization code sent to their smartphone. What can be concluded from this scenario?
- A. FinanceX has implemented an integrity control that avoids the involuntary corruption of data
- B. FinanceX has incorrectly implemented a security control that could become a vulnerability
- C. FinanceX has implemented a securityControl that ensures the confidentiality of information
Correct Answer: C 🗳️
Explanation: Only visible for TestPassed members. You can sign-up / login (it's free).
An organization has decided to conduct information security awareness and training sessions on a monthly basis for all employees. Only 45% of employees who attended these sessions were able to pass the exam.
What does the percentage represent?
- A. Measurement objective
- B. Attribute
- C. Performance indicator
Correct Answer: C 🗳️
Explanation: Only visible for TestPassed members. You can sign-up / login (it's free).
Viewing page 1 out of 25 pages.
Viewing questions 1-5 out of 123 questions.


 Allen

 Arlene

 Amelia
 Matthew
 Rodney
 Elsa
 Olga
 Kevin
 Fitzgerald
 Ursula
 Morton

 Cherry
 Naomi
 Abigail
 Joshua
 Page
 Claire
 Gale